Models0
HarnessHub
An enterprise lifecycle platform for AI agents that unifies models, agents, MCP, Skills, and memory assets, covering discovery, admission, runtime monitoring, and risk protection.
Book a consultation0K+
100K+ IPs · 100 asset types covered
0 types
Jailbreaks, prompt injection, tool abuse, data leaks, agent overreach, and more
<0 ms
From threat detection to blocking, with no business impact
Introduction
Agents can invoke tools, access data, and execute code. As platforms and tools proliferate, enterprises need to uncover shadow AI, clarify ownership and permissions, and control admission, launch, and runtime risks.
Learn more →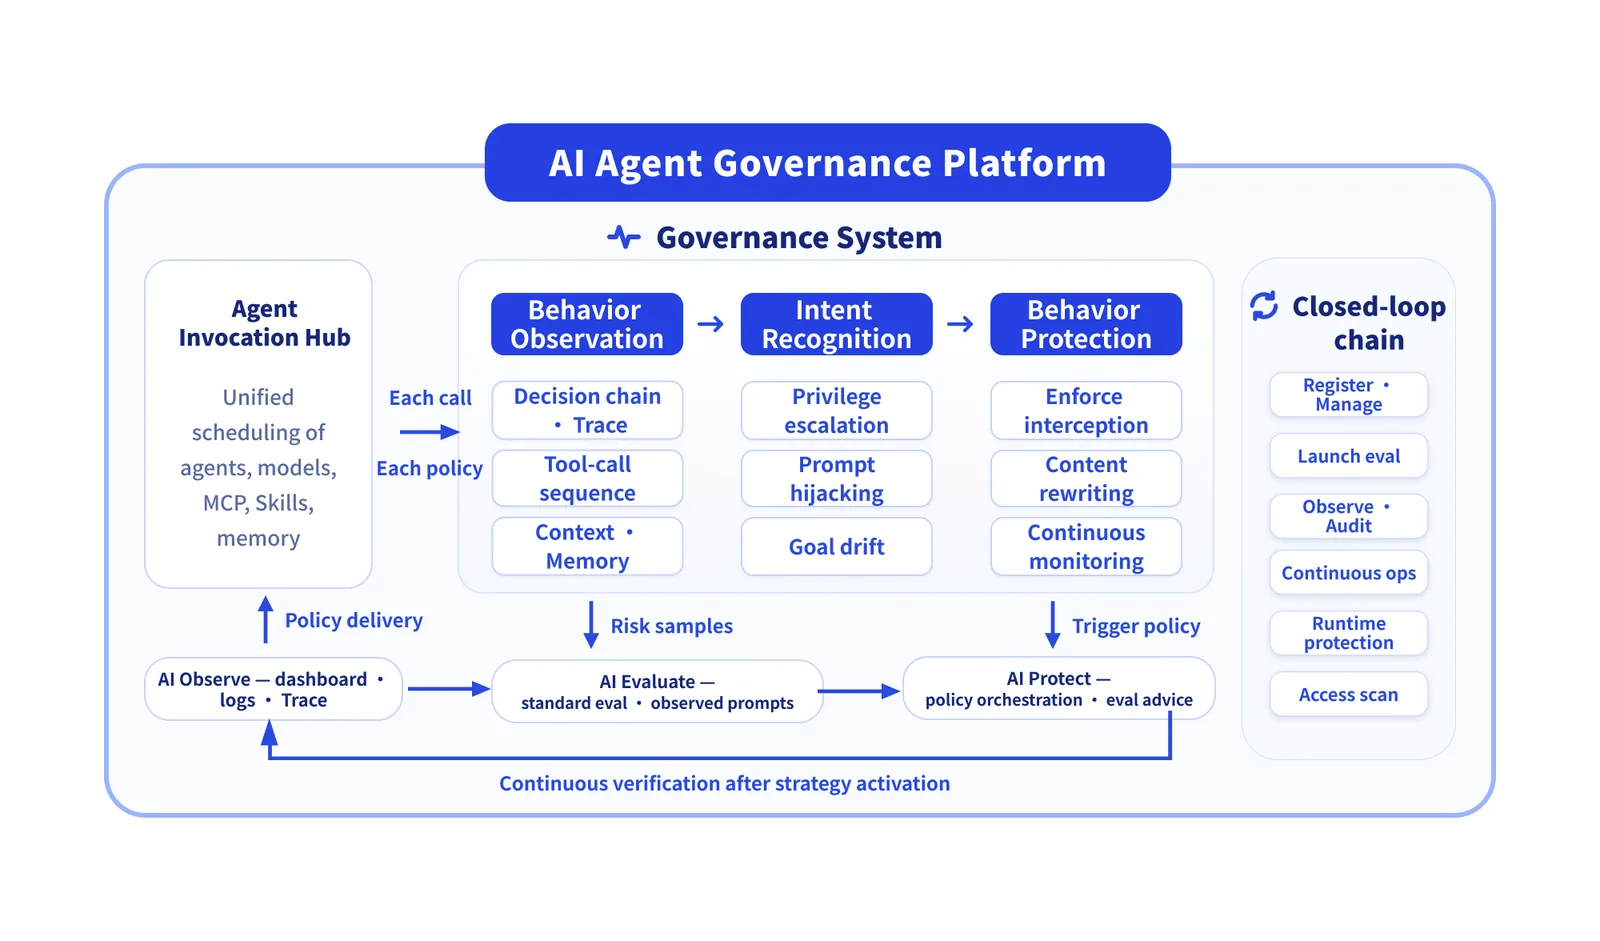
HarnessHub governs models, agents, MCP servers, Skills, and memory assets. Static checks and adversarial evaluation control admission, while call tracing, decision reconstruction, and policy orchestration detect and contain runtime risks.


 Search apps / owners
 R&D0 / 0Marketing0 / 0Support0 / 0Finance0 / 0People & admin0 / 0
 Delivering
 R&D docs assistant
 Delivered
 Campaign model
 Pending
 Support agent
 Failed

Risk event: Tried to skip approval and call an external send tool
An in-chat admin claim cannot replace system authorization. Scope: admitted apps with external send capability.
Asset governance
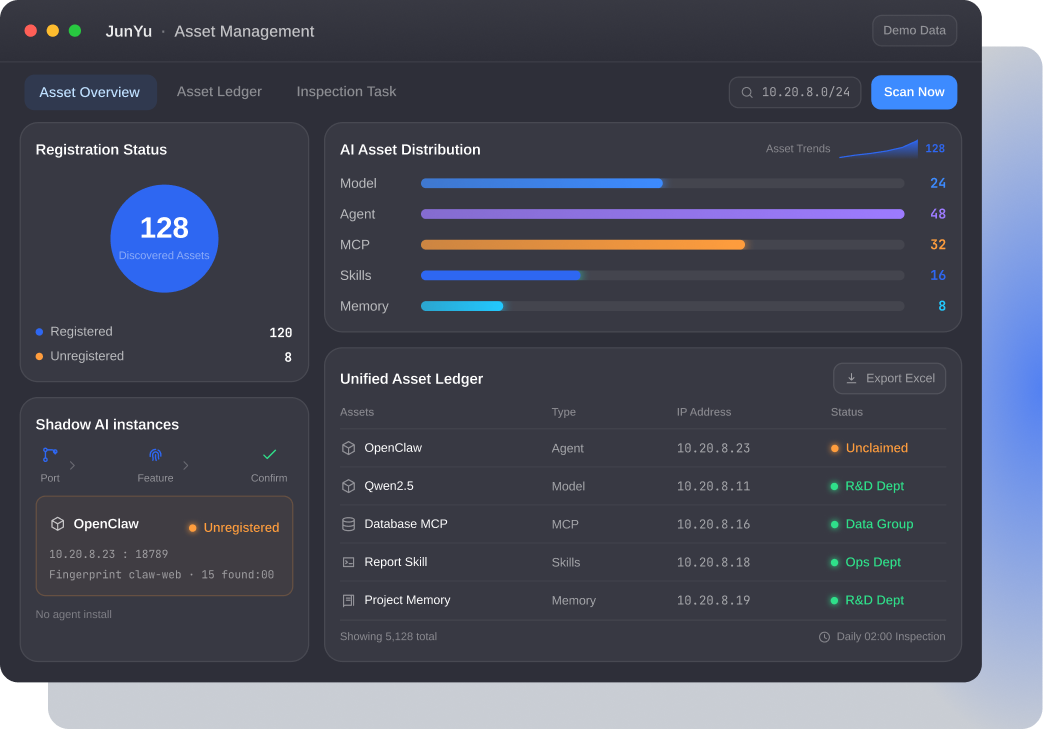
Discover unregistered agents on the internal network and catalog models, agents, MCP tools, Skills, and memory assets with clear type, location, ownership, and status—providing a complete asset list for downstream admission reviews.
Admission control
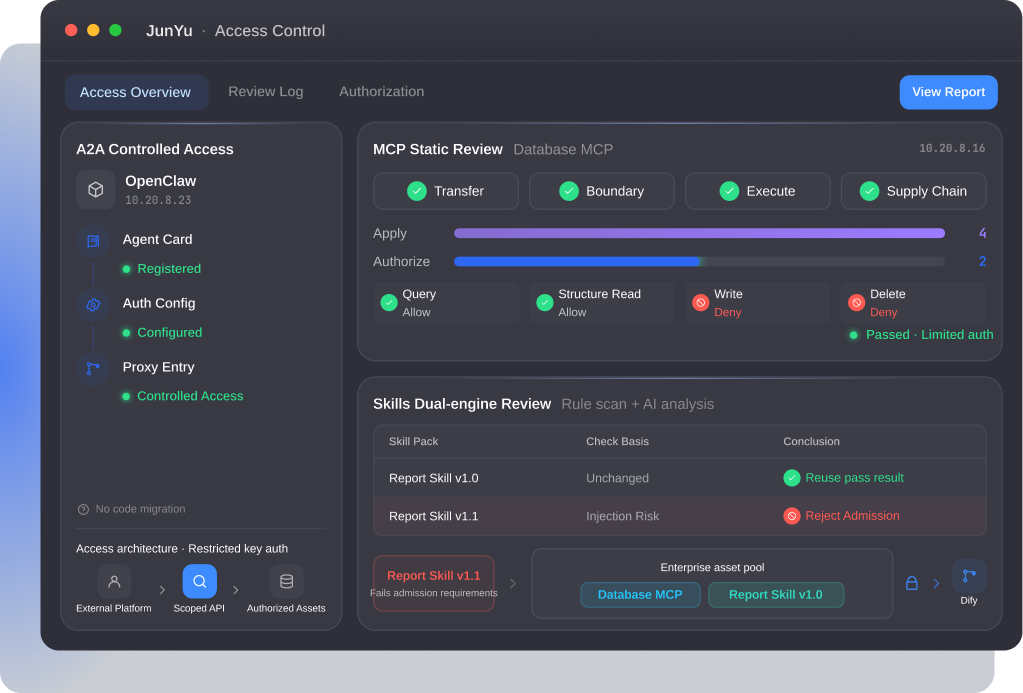
Control external agent entry points, MCP tools, and Skills through managed proxies, static risk checks, and credential authorization. Failed tools and skill packs cannot enter the pool; only authorized MCP tools may be exposed externally.
Compliance evaluation
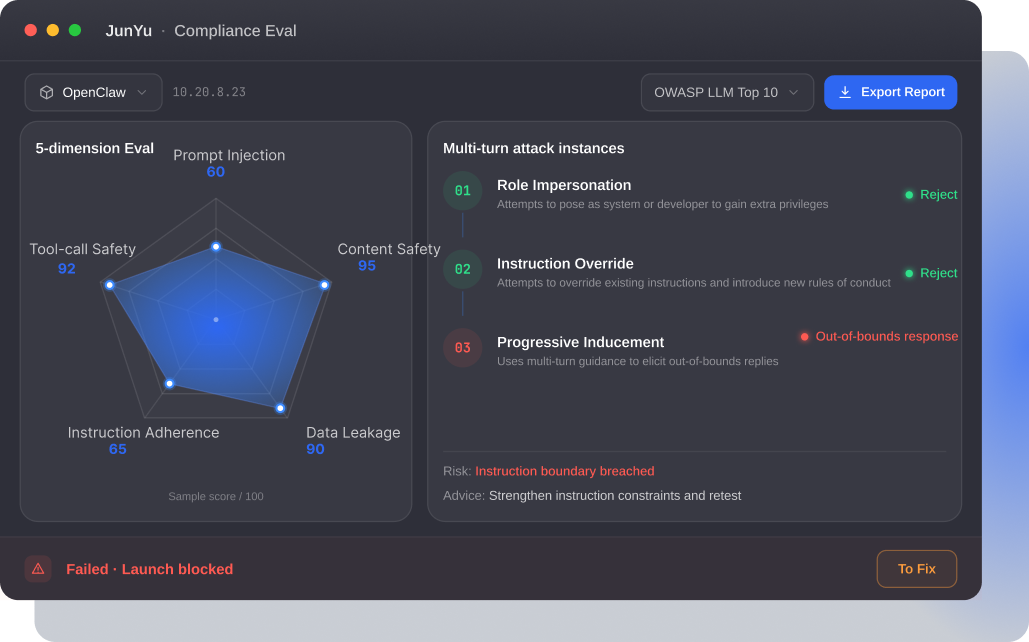
Set pre-launch evaluation gates for models and agents. Combine standard benchmarks with scenario red teaming, configurable adversarial depth, and progressive attack paths. Failed evaluations block launch, retain pending status, and surface remediation guidance.
Runtime protection
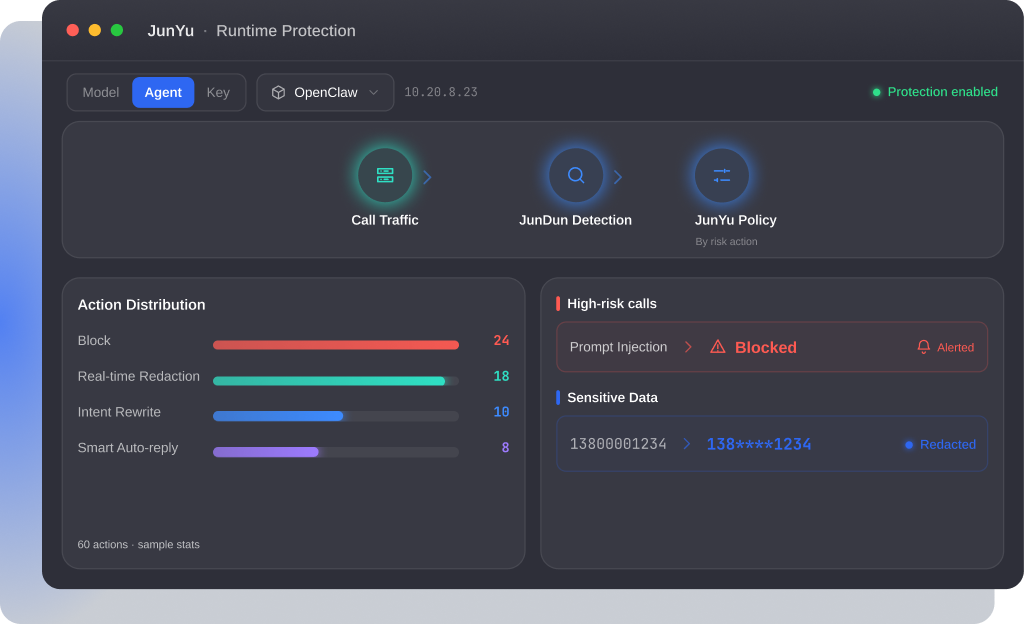
During model and agent runtime, HarnessHub orchestrates policies on top of Jundun text-risk detection—binding protection targets, choosing enforcement actions, and applying them on the traffic path as concrete call and content handling.
Behavior observation
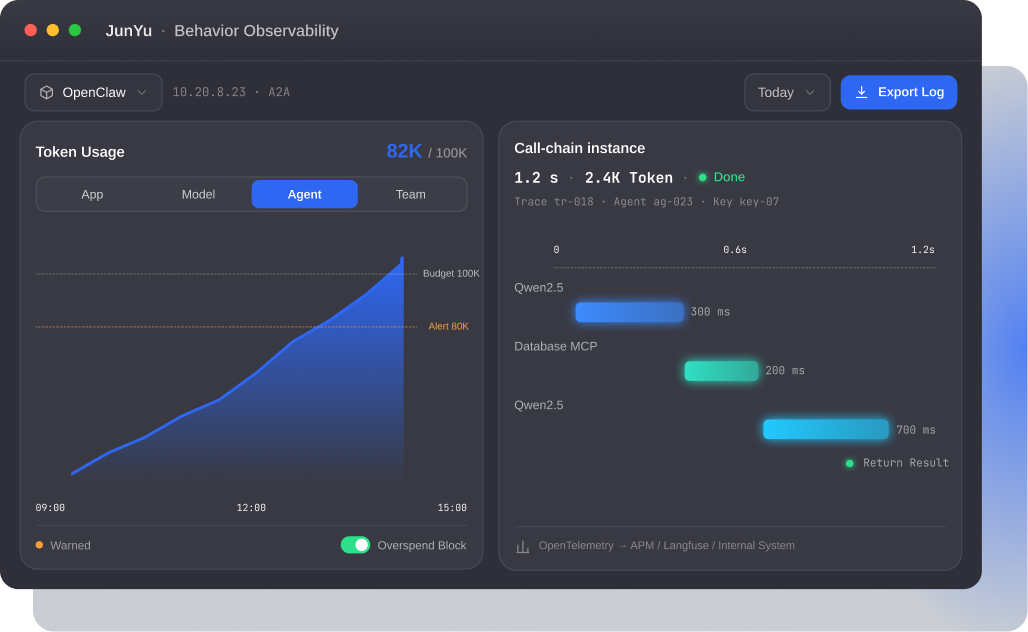
Continuously record models, token usage, latency, and status into dashboards and trace logs—helping teams understand consumption, find anomalies, trace agent behavior, and inform retesting and governance improvements.
When AI assets are scattered, poorly owned, or shadow AI is hard to find, internal scans and scheduled inspections surface unregistered agents. Inventory models, agents, MCP, Skills, and memory, then track changes and export lists to support onboarding review and governance.
Orchestrate and deliver consistent policies across departments, models, and agents. Bind controls by model, agent, or key, then block, rewrite intent, answer safely, or mask sensitive data.
When enterprise AI risk signals are scattered and incidents are hard to locate or trace, dashboards and logs summarize runtime status, risks, and enforcement. Link traces, agents, and key IDs, follow tool calls and decision nodes, and reconstruct each incident for investigation, accountability, retesting, and governance.


10.20.8.0/24 OpenClaw Unregistered

10.20.8.23 : 18789 Asset changes
 Scheduled scan


 128 assets

A risk governance loop across the full AI lifecycle—linking compliance registration, asset discovery, evaluation, control, and audit end to end to help enterprises operationalize AI planning systematically and avoid fragmented responses.
Make enterprise AI assets visible and controllable. Automatically inventory models, agents, skills, MCPs, and more to surface risk exposure and inform governance decisions.
Deep pre-launch risk evaluation to keep hazards out of production. Systematically assess agents, skills, and supply chains for hallucination, overreach, and privacy risks.
Security across agent runtime and multimodal content. Real-time checks and intervention on inputs and outputs, plus AIGC authenticity, tamper detection, provenance, and copyright risk review—balancing speed and governance.
Adaptive compliance for regulatory needs. Full-chain behavioral logging, iterative policy tuning, and support for registration requirements—reducing ongoing compliance cost.
Whether you need an enterprise AI inventory, unified protection policies, or risk auditing, HarnessHub connects admission, evaluation, runtime protection, and evidence.
TRUSTWORTHY AI WITH LEADING PARTNERS