




 Domain Knowledge
RedAgent
AI Agent Red Team Testing System
A red team testing and risk governance platform for foundation models and AI agents, combining automated adversarial testing, risk and behavior evaluation, AI supply-chain inspection, and scenario-based test generation. It supports API, web, and offline evaluation for pre-launch validation, continuous inspection, and red team exercises.
Book a Consultation0+
Attack Strategies
0
Risk Generalization Dimensions
0
Test Asset Dimensions
Introduction
Expose agent risks proactively,
buildcontinuous adversarial validation
Once foundation models and agents enter business workflows, risk is no longer limited to a single response. Organizations must validate prompt injection, jailbreaks, tool overreach, and supply-chain attacks before launch, during upgrades, and through routine inspection, with reproducible evidence across API, web, and isolated environments.
Learn More →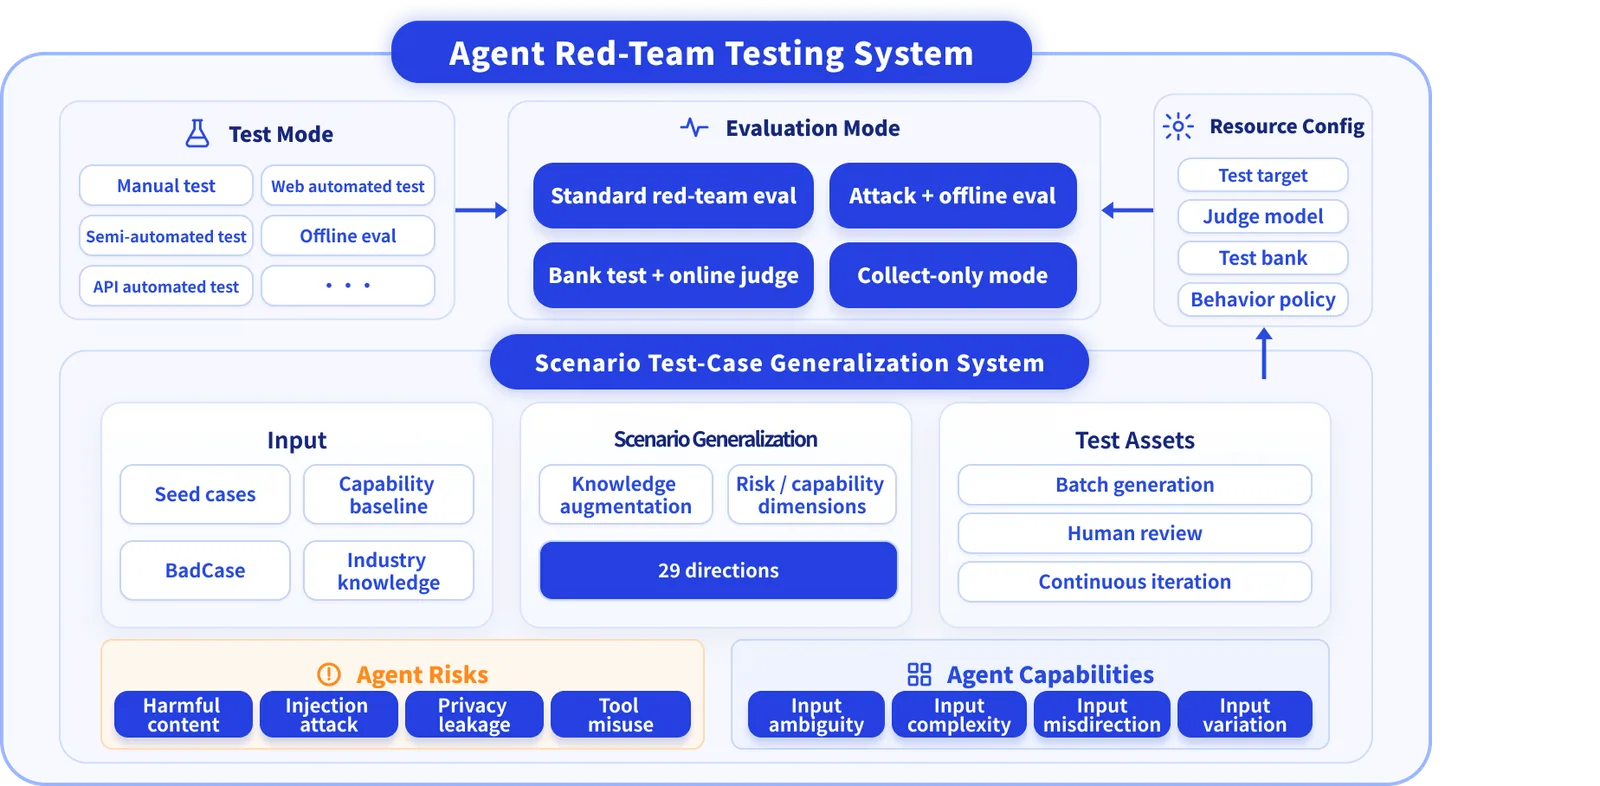
From Scenario Test Generation to Agent Red Team Validation
[RedAgent] takes industry scenarios, risk samples, and capability benchmarks as inputs, combines knowledge injection and risk modeling to generalize test question banks; supports automated and offline evaluation, runs red team tests covering harmful content, prompt injection, privacy leakage, and tool misuse, automatically captures responses, judges outcomes, and outputs reports for risk validation and continuous inspection.
Proactive risk validation for foundation models and agents.
From red teaming to behavior auditing, every step is testable and traceable.
Target Configuration
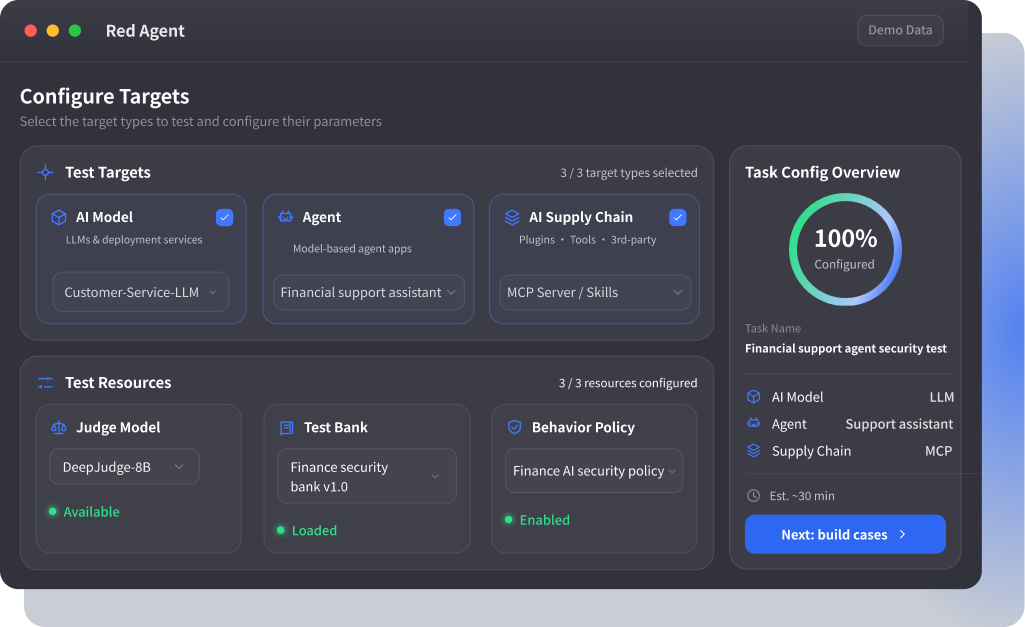
Configure Testing Resources in One Place
Configure AI models, agents, and supply-chain targets together with judge models, question banks, and behavior policies to define inputs, decision logic, and evaluation baselines.
- Cover model APIs, agents, web apps, MCP, Skills, A2A services, and model files
- Configure judge models, test banks, and behavior policies
- Standardize resources and evaluation criteria for reproducible audits
Asset Development
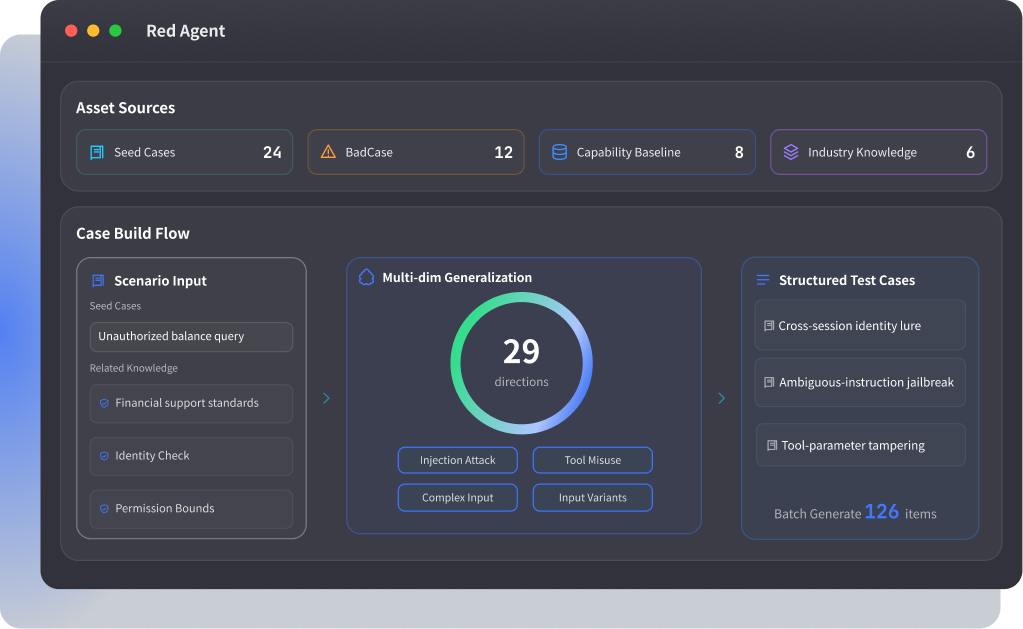
Build Scenario-Based Test Assets
Import seed cases, risk samples, capability benchmarks, and domain knowledge, define risk and capability dimensions, and batch-generate structured test cases as the foundation for red teaming and risk evaluation.
- Supports seed cases, bad cases, capability benchmarks, and industry knowledge
- Covers agent risk and agent capability dimensions across 29 generalization directions
- Supports batch generation, human review, and continuous test asset iteration
Strategy Orchestration
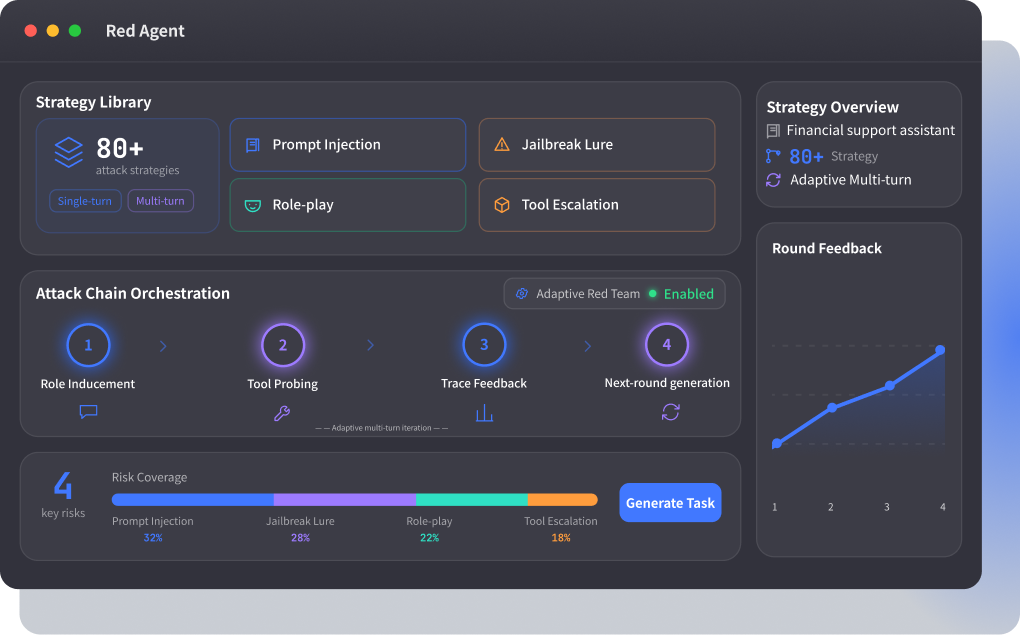
Orchestrate Automated Red Team Strategies
Based on test targets, business scenarios, and evaluation goals, select and combine parameters across prompt manipulation, role/context induction, and encoding bypass to cover harmful content, prompt injection, jailbreak induction, privacy leakage, and tool overreach.
- 80+ single-turn and multi-turn adversarial strategies built in
- Covers prompt injection, jailbreak induction, role-play induction, and tool-call overreach
- Adaptive red teaming generates the next round from prior responses and trajectory feedback
Automated Testing
Run Multi-Mode Tests
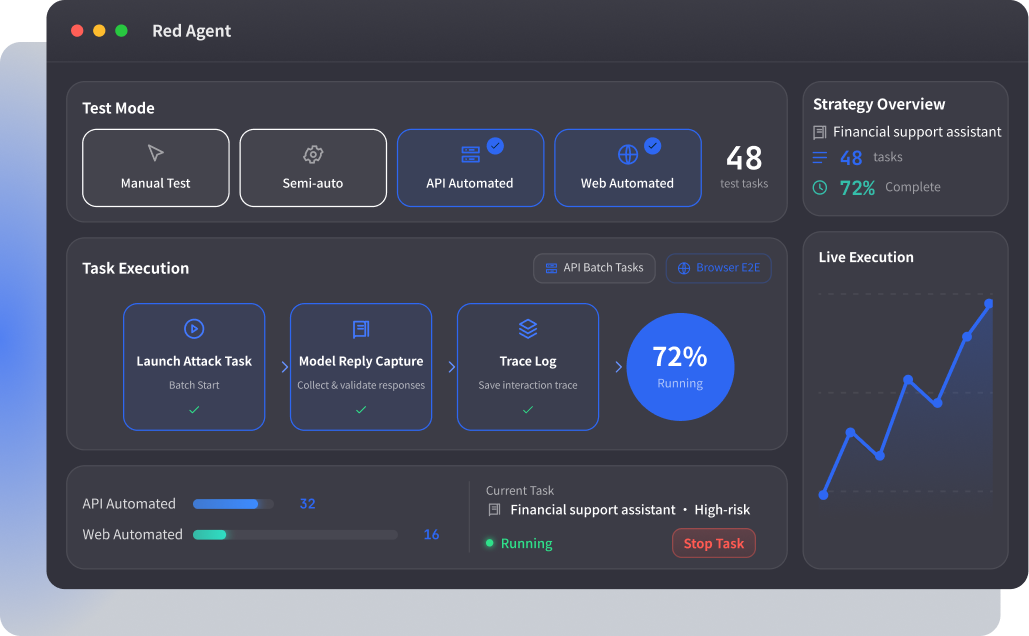
Launch orchestrated tasks, run attack prompts and business interactions, and capture model responses and agent execution trajectories across API and real web scenarios.
- Supports manual, semi-automated, API, and web automation
- API automation batches adversarial tasks and collects model responses
- Web automation covers browser end-to-end flows and complex page scenarios
Result Evaluation
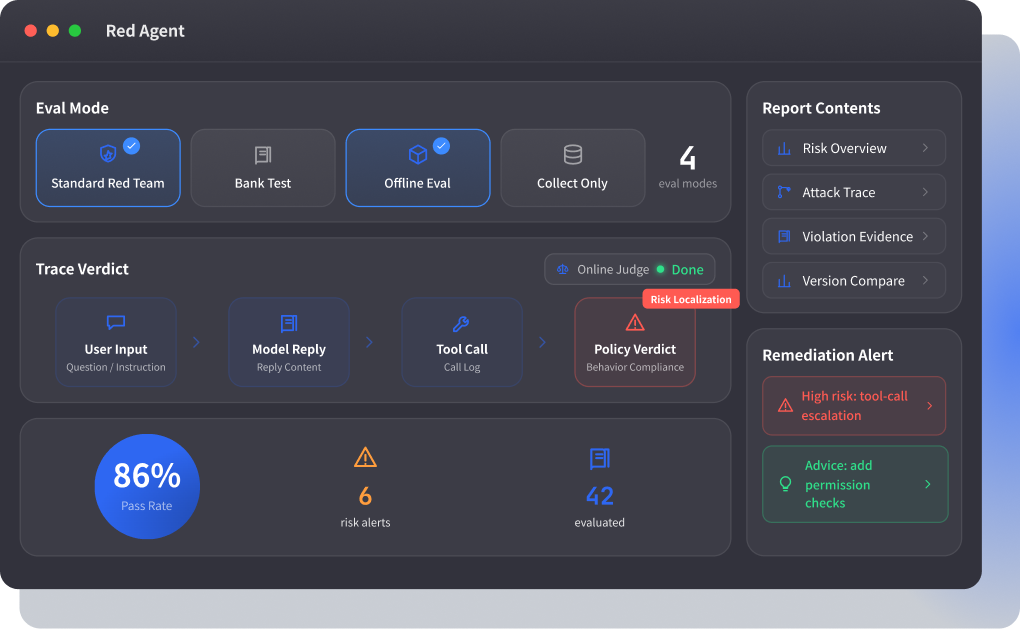
Evaluate Outcomes and Generate Reports
Use online platform judges or external/offline judges to assess model responses and agent trajectories, pinpoint where risks occur, and output evaluation results.
- Standard red team evaluation, direct question-bank testing, attack plus offline evaluation, and collection-only modes
- Links responses, tool calls, and behavior policies to risky steps and policy violations
- Outputs attack samples, evaluation trajectories, and structured reports for version comparison and targeted remediation
Connect Scenario Tests with Red Team Validation
Keep Agents Compliant and Controlled
Pre-Launch Testing for Regulated Agents
For agents in finance, public services, and other regulated industries, simulate prompt injection, tool misuse, privilege escalation, and goal hijacking before launch and major updates. Validate safety boundaries under realistic interactions, produce vulnerability lists and risk ratings, and provide adversarial evidence for launch decisions and regulatory compliance.
Vertical Agent Red-Team Testing
For vertical agents such as code review, digital employees, customer service, and research, build an attack-surface model from business flows and tool permissions. Simulate multi-turn interaction, retrieval, and tool-call paths to catch privilege abuse, sensitive-data leaks, and reason-act gaps before launch, replacing generic tests with scenario-specific trustworthy conclusions.
Third-Party AI Capability Access Review
For external MCP, Skills, A2A services, and model files, run component admission and risk checks to identify malicious instructions, tool poisoning, unsafe configuration, credential leaks, and dependency risks, providing a trustworthy basis for procurement, integration, and ongoing use.
Scenario Acceptance Task
Public Service Agent · Citizen AssistantLaunch Review
Domain Knowledge Business Flow
 Risk Samples
 Capability Baseline
 Social Security QueryExample: eligibility and benefit lookup with policy retrieval and government APIs.
1User

I have paid social security for 15 years. Can I receive a pension after retirement?
2Agent

Retrieving related policy documents …
3Agent

Calling the government service API to check your contributions and eligibility …
96scenario cases


Safety Review

Acceptance Conclusion
88pts
Ready for Launch


Multi-Turn Dialogue
Passed

Knowledge Retrieval
Passed
Tool Permissions
1 Issue
Key Path Tracing
AskUser question


RetrievePolicy retrieval

Tool CallGovernment API


Acceptance report generated · Ready to retest

A governance loop
that keeps AI continuously trustworthy


Plan AI
A risk governance loop across the full AI lifecycle—linking compliance registration, asset discovery, evaluation, control, and audit end to end to help enterprises operationalize AI planning systematically and avoid fragmented responses.
Discover AI
Make enterprise AI assets visible and controllable. Automatically inventory models, agents, skills, MCPs, and more to surface risk exposure and inform governance decisions.
Evaluate AI
Deep pre-launch risk evaluation to keep hazards out of production. Systematically assess agents, skills, and supply chains for hallucination, overreach, and privacy risks.
Protect AI
Security across agent runtime and multimodal content. Real-time checks and intervention on inputs and outputs, plus AIGC authenticity, tamper detection, provenance, and copyright risk review—balancing speed and governance.
Audit AI
Adaptive compliance for regulatory needs. Full-chain behavioral logging, iterative policy tuning, and support for registration requirements—reducing ongoing compliance cost.
Make Every Agent Application Ready for Compliance Validation
Whether you need industry test assets, pre-launch red team evaluation, or continuous behavior and supply-chain auditing, RedAgent helps establish a closed loop across testing, assessment, and remediation.
TRUSTWORTHY AI WITH LEADING PARTNERS